How we protect your business and your data.
Security is built into how we work, from the first demo to long-term support. Here is what you can expect from us, in plain language.
Six promises we make to every client.
These are drawn from our privacy and corporate policies, which apply to every engagement.
Secure by default
Multi-factor authentication on every account, Conditional Access, encrypted company devices and encryption in transit and at rest.
Canadian data residency
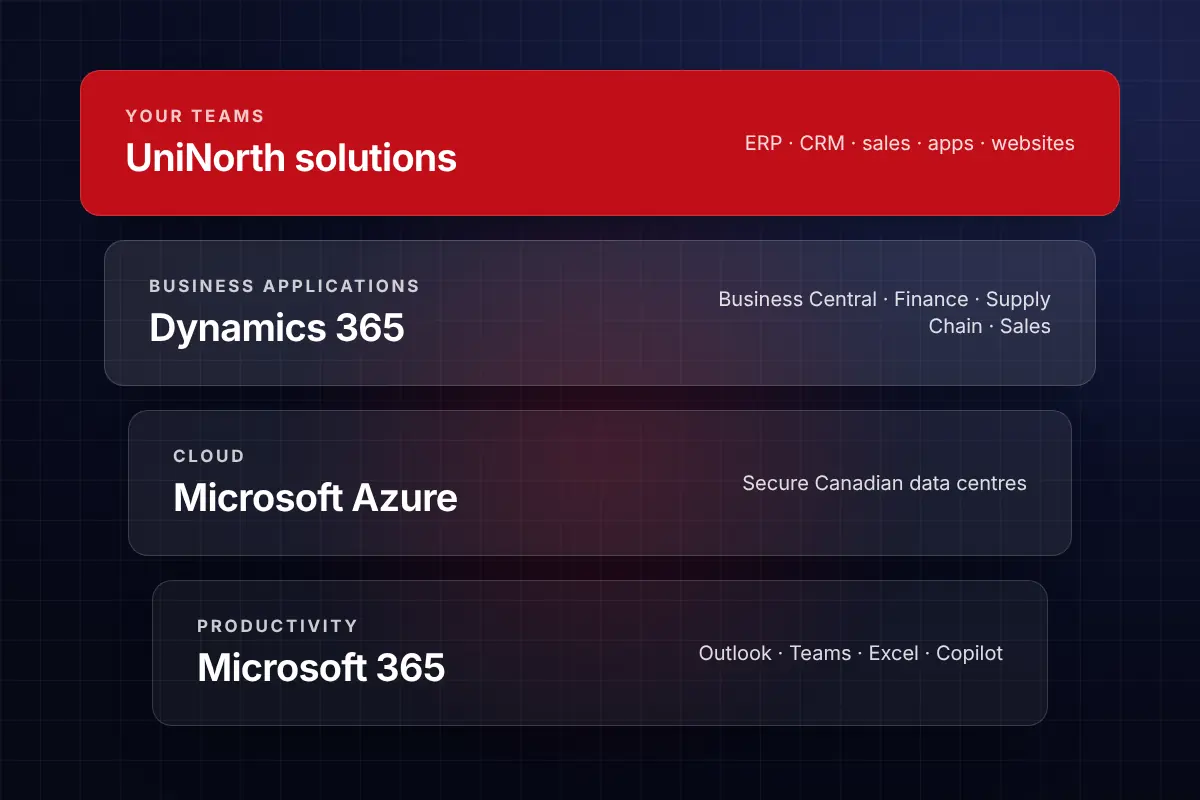
Dynamics 365, Microsoft 365 and Azure can be deployed in Microsoft data centres in Canada.
Least-privilege access
Time-limited, role-specific admin access to your tenant. We never ask for or store your passwords.
Your data stays yours
Client data is used only to deliver the agreed services. Never for our marketing, and never to train AI models.
Demos use sample data
Demonstrations use sample data, and trial environments are scoped in writing before any of your information is used.
Prompt breach notification
If an incident affects your data, we notify you without undue delay and within any time frame in our contract.
Configured to Microsoft security guidance.
Every environment we implement or manage follows the same controls we use to run UniNorth.
- Identity
- Multi-factor authentication, Conditional Access and restricted guest access
- Administration
- Granular delegated admin privileges (GDAP), reviewed regularly and removed when no longer needed
- Devices
- Company-managed, encrypted devices with remote wipe
- Environments
- Separate demo, test and production environments
- Data residency
- Canadian Microsoft data centres available for Dynamics 365, Microsoft 365 and Azure
Technology only protects you when the people and processes around it are disciplined.
Trained team
Security and privacy training for everyone at onboarding and every year after.
Confidentiality
Everyone who works on client data is bound by confidentiality obligations, and NDAs are available on request.
Vetted suppliers
We review service providers' security before using them for personal or client data.
Responsible AI
Business-grade AI tools only, with a person reviewing every output used in client work.
Read the details.
The full privacy policy and corporate policies.
How we collect, use, protect and retain information, and how to reach our Privacy Officer.
Read the policies
How we handle demos, trials and proofs of concept.
Sample data, recordings, trial environments and what happens to your information afterwards.
Read the section
Security incidents and breach notification.
How we contain, assess and report incidents under PIPEDA and Quebec law.
Read the sectionWhere is our data stored?
Dynamics 365, Microsoft 365 and Azure can be deployed in Microsoft data centres in Canada. We confirm the data location for each service in your proposal.
Do you need our passwords?
No. In Microsoft tenants we use granular delegated admin privileges with time-limited, role-specific permissions, and we never ask for or store your passwords.
Will you sign an NDA or a data processing addendum?
Yes. On request we sign a non-disclosure agreement and a data processing addendum covering confidentiality, security and data handling.
Do you use our data to train AI?
No. Client data is never used to train AI models, and we use business versions of AI tools that do not train on our prompts or data.
What happens if there is a security incident?
We act quickly to contain and assess it. If it affects your data, we notify you without undue delay and within any time frame in our contract, and we meet our reporting obligations under PIPEDA.
Want an expert view of your Microsoft security?
We will review your identity, devices and data protection and give you a prioritized plan.